An agent is asked to help with pending orders. It finds a wrong address and decides to correct it. The intention is useful; the important question is whether it had permission.
When AI moves from answering to acting, every access path needs a visible boundary.
Controls for AI agents are technical and operational rules that determine which information an agent may read, which actions it may take, when it must request approval and how activity is recorded.
Model intelligence does not define authority
An agent may interpret a request correctly and still lack authority to modify a record, send a message or initiate a payment.
Security must cover the complete process: identity, data, tools, approvals, records and recovery from errors.
Seven essential controls
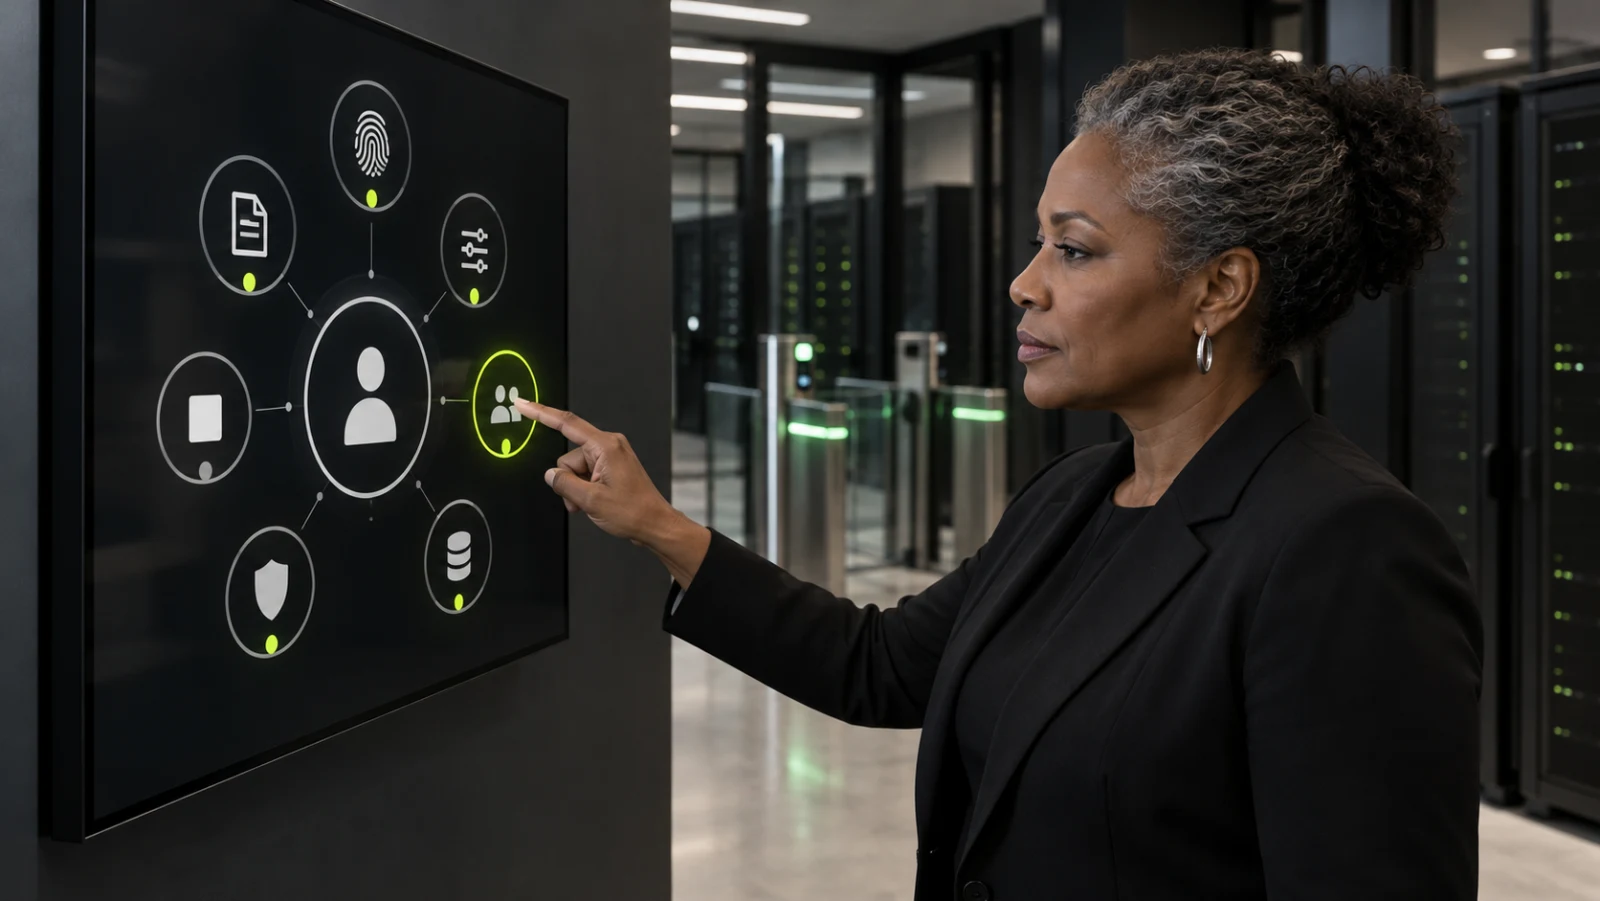
- A distinct identity attributes every action.
- Minimum access limits data to what is required.
- Bounded tools restrict functions to the purpose.
- Human approval protects sensitive actions.
- Operating limits define amount, frequency, time or scope.
- Records preserve inputs, decisions and actions.
- Recovery allows the business to stop, reverse or escalate.
A small change with real consequences
Composite example: this scenario is not a result attributed to a specific Ainoa customer.
A support agent notices that an order has an incomplete phone number. It can request confirmation, suggest a correction and prepare the change.
A safe design prevents automatic modification of critical data without validation. The agent helps the process move forward while authority remains defined by the company.
How to design controls from the process
- List the data and actions required to achieve the objective.
- Classify decisions as informational, operational or sensitive.
- Separate read and write permissions.
- Define approval thresholds and owners.
- Test errors, ambiguous instructions and malicious data.
- Review records and adjust permissions using evidence.
Mistakes that expand risk
- Sharing a person's credentials with the agent.
- Allowing write access when reading is sufficient.
- Treating a text instruction as the only control.
- Storing sensitive data without a defined need.
- Ignoring what happens when an integration fails.
How to measure whether controls work
- Actions requiring approval.
- Attempts blocked for exceeding scope.
- Errors recovered without affecting the source system.
- Time required to investigate an action.
- Permissions that are no longer necessary.
Frequently asked questions
Does an agent need its own identity?
A distinct identity is recommended because it separates permissions and attributes actions.
Should humans approve everything?
No. Approval should focus on sensitive, irreversible or high-impact actions.
Does MCP automatically solve security?
No. MCP enables connections; the business still defines authentication, permissions, validation and records.
A useful agent also knows where to stop
Trust does not come from promising that an agent will never fail. It comes from boundaries, visibility and recovery.
Ainoa develops Custom Intelligent Agents and Custom Administrators with rules adapted to the operation.
Talk to Ainoa. We review a real process, identify its risks and design an agent with the right authority.